Livestream coder alleges stolen keys were used to run Fable 5.1 swarms
An X post alleges that someone took its "keys" during a livestream coding session and used them to run Claude Fable 5.1 sessions, but provides no details confirming the activity.
By Ryan Merket · Published
Primary source: X
Why it matters
The post raises a security concern for people running AI tools with credentials, but does not establish what keys were taken, what systems were accessed, or whether any damage occurred.
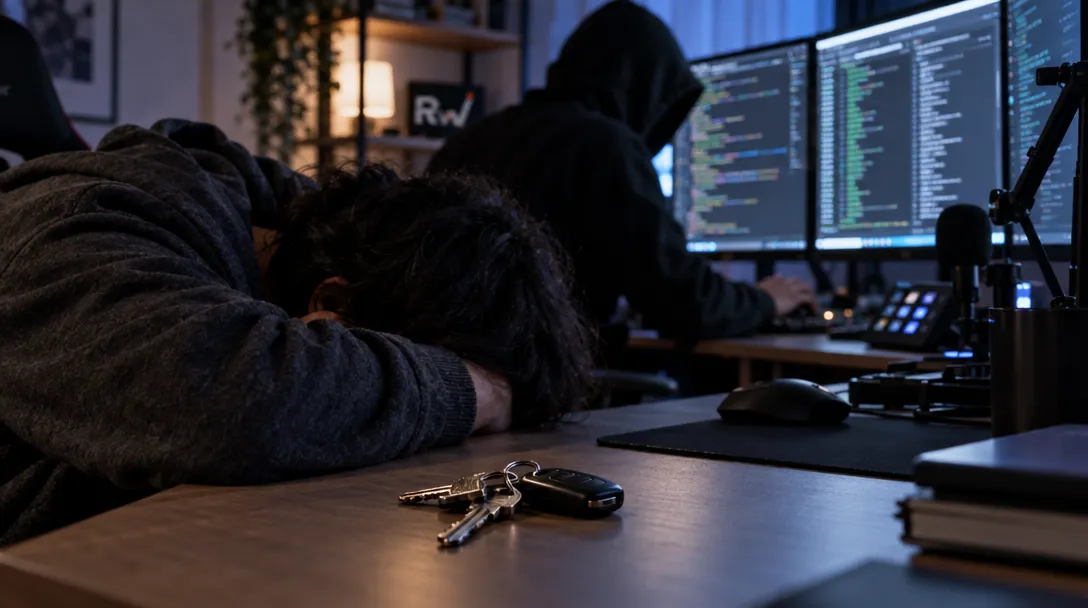
An X account alleges that someone took its "keys" while its operator was unconscious during a livestream coding session and used them to run multiple Claude Fable 5.1 sessions. The post does not specify what kind of keys were involved or provide details establishing what happened.
The account, Just_Lingonberry_352 (@JustLingonberry), made the claim in a post on X. It says the operator "passed out" during the session. The post does not identify the alleged person, describe the activity as API use, or state whether any account, repository, or billing information was affected. Its use of "swarms" is also left undefined.

Anthropic introduced Claude Fable 5.1 on September 1st, 2026, describing it as a model for coding and knowledge work. The model is available through Anthropic's products and API, as well as cloud marketplaces, according to Anthropic's product information. That context makes unauthorized access to credentials a plausible concern for users running AI workloads, but it does not verify this particular allegation or establish that Anthropic's systems were involved.
The post gives no details about how access was obtained or whether the alleged activity generated charges or changed code. It remains an unverified claim, not confirmation of a breach or evidence that Claude Fable 5.1 or Anthropic infrastructure was compromised.